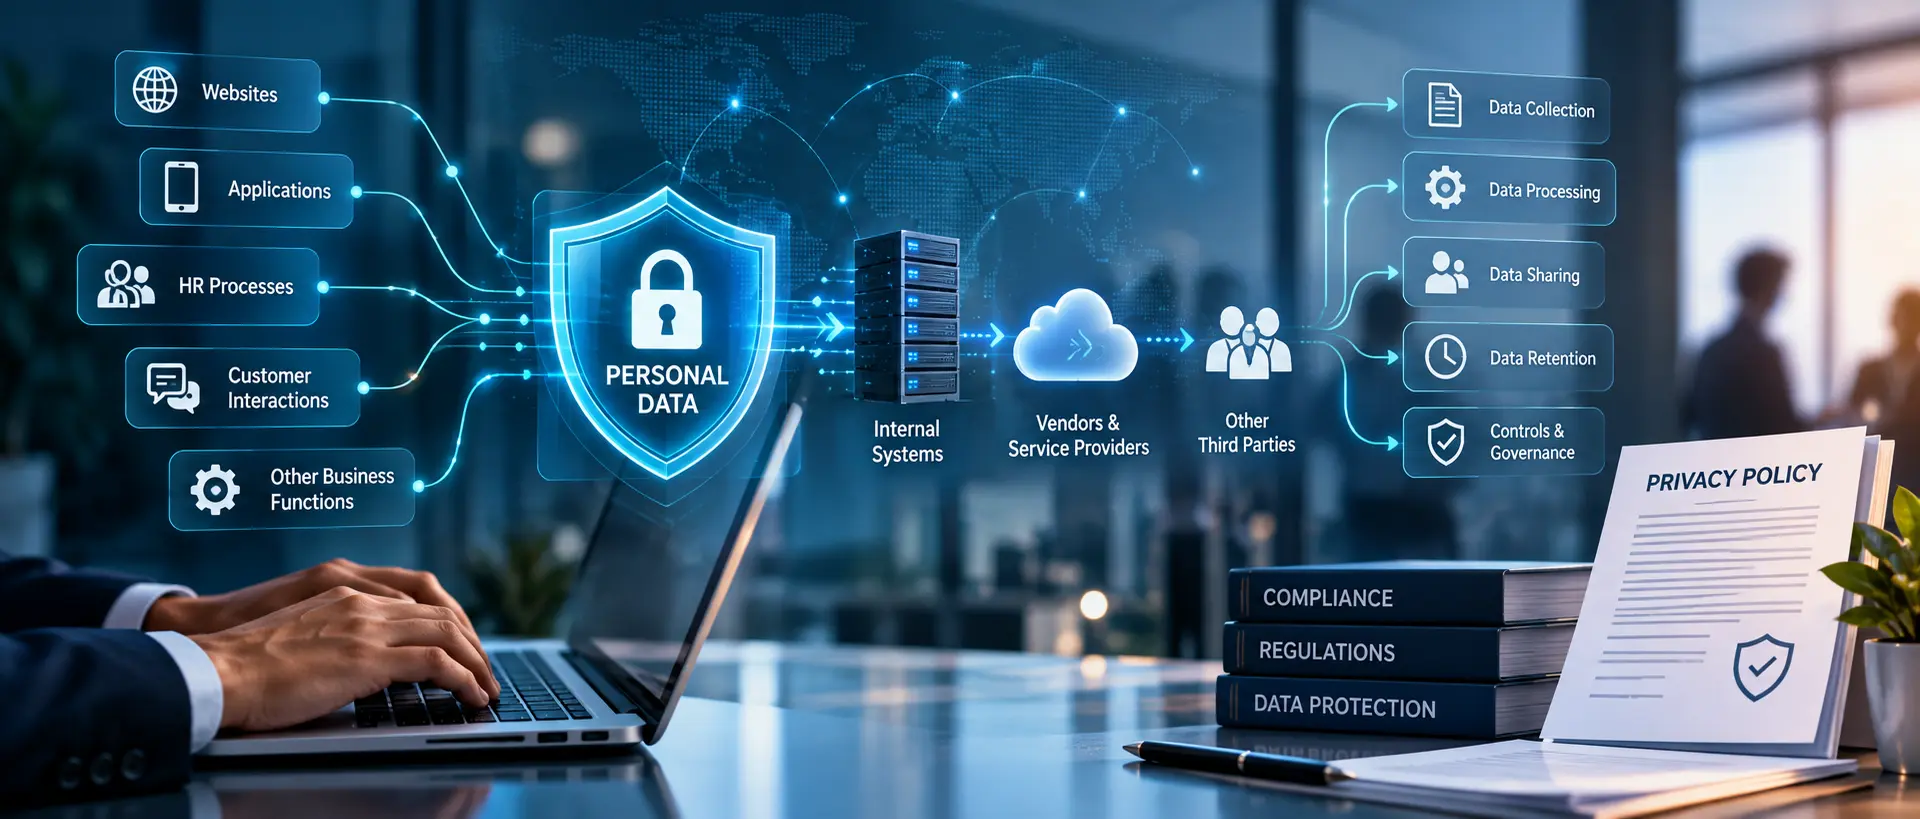
It sits across the systems, teams, vendors and processes that collect, use, share and retain personal data. DPDP compliance begins with knowing what personal data your organization holds, where it moves, who processes it, and what controls govern it.
Aegis works across those touchpoints to turn DPDP requirements into controls the organisation can actually operate.
Personal data is collected through websites, applications, HR processes, customer interactions and other business functions. It is then processed across internal systems and shared with vendors, service providers and other third parties.
The resulting compliance challenge is operational: organisations need visibility into where personal data is collected, how it is processed, who it is shared with, how long it is retained and what controls govern each stage.
A privacy policy documents obligations. It does not by itself establish that those obligations are being followed across the data lifecycle.
A breach is not the point at which an organisation should begin deciding who does what. The response framework needs to be established beforehand with clear escalation, assessment, containment, notification and remediation responsibilities.
DPDP compliance is not only about preventing or controlling data misuse. It is also about having a defined organisational response when an incident occurs.
Aegis helps establish breach response protocols and provides incident support when personal-data incidents occur.
Response protocols, escalation paths and responsibilities are defined in advance.
The organisation can move from detection to assessment, containment and response without designing the process under pressure.
Aegis covers the work required to move from readiness assessment to privacy programme development, operational oversight, training and ongoing privacy leadership.
Evaluate current data practices against DPDP requirements, identify gaps and prioritise remediation.
Map personal data across systems, business processes, vendors and geographies establishing what is collected, where it is held and who it is shared with.
Assess organisation-wide and department-specific DPDP requirements and develop prioritised compliance roadmaps with responsible owners and implementation timelines.
Establish ownership, accountability and escalation paths for ongoing privacy management.
Build the privacy programme across policies, consent, processing, retention, deletion, vendor management, incident response and training.
Draft and review DPDP-aligned provisions for vendor and processor relationships.
Define internal escalation, containment, investigation and notification procedures before an incident occurs.
Govern and monitor how personal data is shared with vendors and partners.
Monitor privacy compliance through audits, self-assessments, regulatory-change tracking, vendor reviews and remediation.
Deliver role-based privacy training, awareness programmes, assessments and privacy-champion initiatives.
Provide ongoing privacy leadership covering DPIAs, data-principal requests, vendor oversight, breach coordination and management advice.
A Data Protection Impact Assessment examines a proposed or existing processing activity in context the nature of the personal data, purpose of processing, people and systems involved, access and sharing arrangements, and the potential impact on individuals.
The objective is not simply to identify risk. It is to determine whether the processing is appropriately controlled, where additional safeguards are required, and what needs to change before the activity proceeds or continues.
A structured assessment that connects processing activity → exposure → required controls, giving the organisation a documented basis for deciding how higher-risk processing should be governed.
AEGIS takes DPDP from readiness assessment into implemented controls, ongoing monitoring and breach support. Every AEGIS engagement is defined around clear deliverables, timelines and accountability.