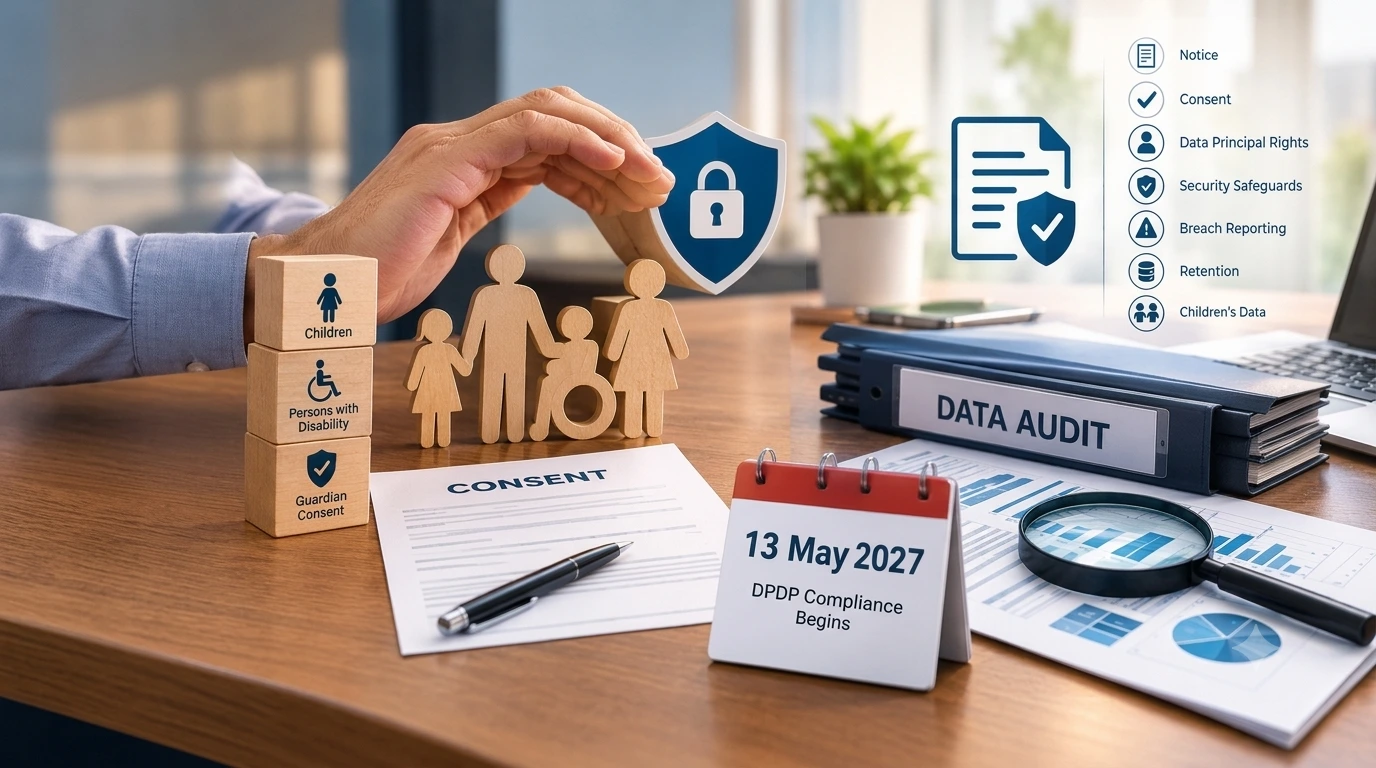
With 13th May 2027, the day when Digital Personal Data Protection compliance begins, getting closer with every passing day, the mental workload on Data Fiduciaries to ensure that their policies, systems and everyday practices are ready for the obligations that lie ahead is increasing. The time available to identify and address gaps is limited and with penalties of up to ₹250 crore, that uncertainty is costly.
Against this backdrop, the Ministry of Electronics and Information Technology (MeitY) issued the Digital Personal Data Protection (Removal of Difficulties) Order, 2026, on 5 October 2026. The Order makes two targeted amendments to the DPDP Act. One clarifies the wording of the provision dealing with consent for certain individuals, while the other removes the ambiguity associated with the periodic audit requirement for the Significant Data Fiduciaries.
Neither amendment introduces an entirely new compliance framework, these changes may look minor but both matter because they clarify how existing obligations should be understood and put into practice. Each one affects how you handle consent or audits, so both belong in your compliance framework. For business leaders, the key question is therefore not simply what wording has changed, but whether the company’s consent processes and audit arrangements reflect that wording.
1. Consent Must Account for People Who Have a Lawful Guardian
The first amendment sets out safeguards for the personal data of the most vulnerable Data Principals, the children and the person with a disability, who have a lawful guardian. Before processing the personal data of a child, or of a person with disability, a Data Fiduciary must obtain verifiable consent from the parent or the lawful guardian, as applicable. In practical terms, Data Fiduciaries need to be able to establish that consent has been provided by the person legally authorised to give it.
The original wording referred to a “child or a person with disability”, without the word “of” before the second category. The 2026 Order inserts that missing word, so the provision now refers to a “child or of a person with disability who has a lawful guardian”. Although the change is only one word, it makes the structure of the provision clearer by placing both categories within the same formulation.
This change is more than a typographic fix. A regulator reads the law as written and acts on them. The stakes are significant because a breach of the additional obligations relating to children’s data under Section 9 can attract a penalty of up to ₹200 crore.
The business implication is that consent processes should not be designed around age verification alone. An age gate may help identify a child, but it will not necessarily identify an adult who has a lawful guardian, which means a company should able to recognise situations in which guardian consent is required and verify that the person providing it has the appropriate authority. Moreover, the consent data must be retained and retrievable as an evidence of the consent obtained since the Act places the burden of proving that consent was given on the Data Fiduciary. This makes consent management more than a one-time screen or form.
The practical test to check whether consent flow systems can handle a user in this category is to assess if the system can:
Identify a user who has a lawful guardian.
Verify that the person giving consent actually holds that authority.
Record the consent so you can produce it on demand, since Section 6(10) puts the burden of proof on you.
2. A Periodic Audit Must Be a Data Audit
The second amendment concerns Significant Data Fiduciaries, a category of companies that carries additional responsibilities under the DPDP Act under Section 10(2). One of its clauses requires an independent data auditor to carry out a “data audit” while one of its other clauses previously referred to a periodic “audit”. The difference in terminology left room for uncertainty about whether the periodic audit had to focus specifically on data protection or could be interpreted as a more general company audit.
The Order replaces “audit” with “data audit” in clause (c)(ii). Both clauses now use the same term, making it clear that the periodic audit is specific to data protection. This change matters because the audit comes round every year. For Significant Data Fiduciaries, this clarification should be reflected in the way audit work is commissioned, scoped and documented. Under the DPDP Rules, 2025, a Significant Data Fiduciary must carry out a Data Protection Impact Assessment as well as an audit every 12 months, and report the key findings to the Data Protection Board. Breaching the Section 10 obligations can also attract a penalty of up to ₹150 crore. The audit therefore needs to examine the company’s data-protection arrangements and provide findings that can inform corrective action and regulatory reporting.
For a Significant Data Fiduciary, a practical review should begin with three things:
Auditor’s mandate: It should refer to data protection by name.
Audit scope: Covers notice, consent, Data Principal rights, security safeguards, breach reporting, retention and children’s data.
Findings: Write them knowing the Board will read them.
Clarity in the Law Must Translate into Clarity in Practice
The DPDP (Removal of Difficulties) Order, 2026, makes two focused changes, but each has a practical consequence for how companies demonstrate compliance. The amendment to Section 9(1) clarifies the wording covering children and persons with disabilities who have a lawful guardian, while the amendment to Section 10(2)(c)(ii) expressly identifies the periodic requirement as a data audit.
For management teams, the next step is to turn these clarifications into specific checks of existing processes, responsibilities and records. Reviewing consent workflows, confirming the scope of audit engagements and assigning ownership for corrective action now can help companies address gaps in a structured way before the principal DPDP compliance deadline of 13th May 2027.
Two changes, and neither requires a new compliance system but both make existing obligations harder to argue around. Section 9(1) now clearly covers a person with disability who has a lawful guardian, on the same footing as a child. Section 10(2)(c)(ii) now clearly calls for a data audit.
The next steps for a company are simple. Review the consent flows, revisit their audit mandates and fix the gaps, before the Data Protection Board finds them. On 13th May 2027, the wording of the statute is what the companies will be held to.